Imagine sending money on a faster, cheaper version of Ethereum. You get your confirmation in seconds instead of minutes. But how do you know the network isn't lying to you? That is the core problem that Rollup Security solves. Rollups are the primary way Ethereum scales up, handling over 65% of all transactions today. They move heavy computation off the main chain but keep data on it for safety. The magic ingredient that makes this trustless is the proof system-either a fraud proof or a validity proof.
The Two Ways to Prove Truth
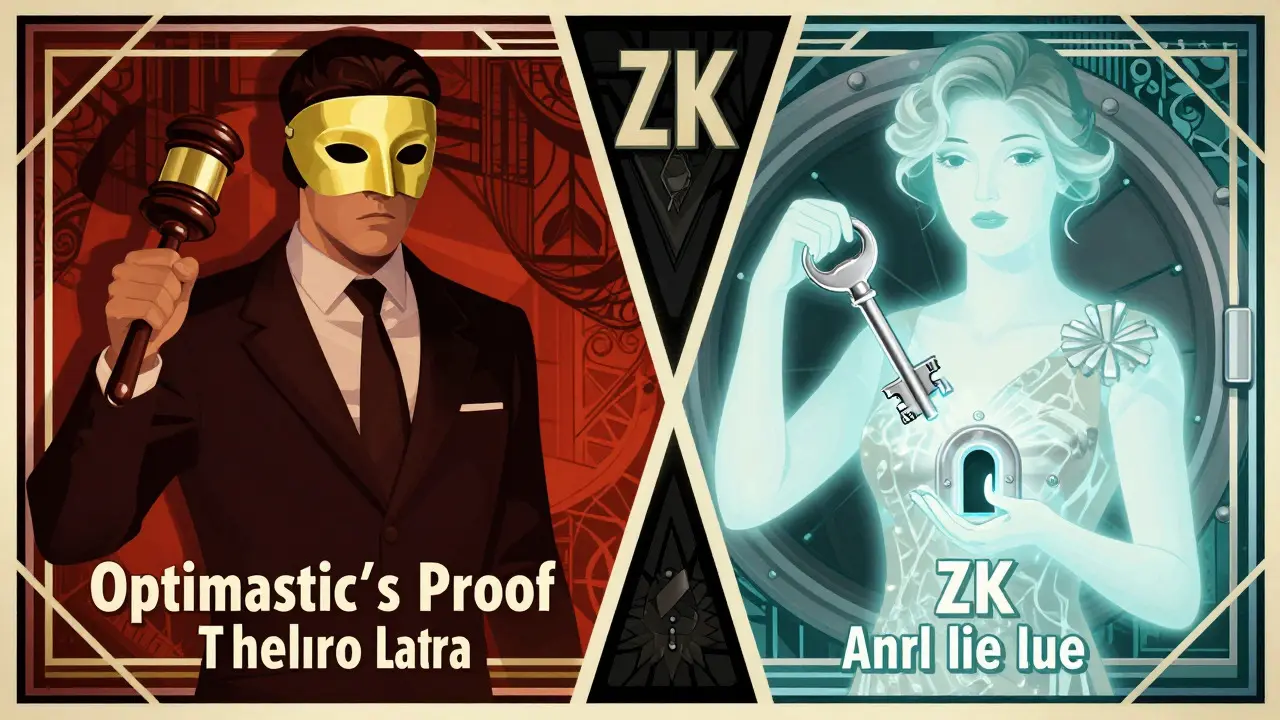
In the world of Layer 2 scaling, there are two main architectures: Optimistic Rollups and ZK Rollups. They both aim for the same goal-security inherited from Ethereum-but they use completely different logic to get there. Understanding the difference is key to understanding why one might be better for your specific use case.
Optimistic Rollups assume everything is correct until proven otherwise. This is similar to how traditional banking works; you assume the bank didn't steal your money unless you audit their books. If someone finds an error, they submit a "fraud proof" to the main Ethereum chain. If the proof is valid, the bad transaction is reverted, and the cheater loses their bond. Projects like Arbitrum and Optimism use this model. It’s simple to build but requires a waiting period (usually 7 days) to ensure no one challenges the state.
ZK Rollups, on the other hand, provide mathematical certainty before anything settles. Instead of assuming correctness, they generate a cryptographic certificate called a validity proof (using ZK-SNARKs or STARKs). This proof mathematically verifies that every transaction in the batch was valid. If the proof checks out on Ethereum, the state is final instantly. No waiting. No challenge period. Projects like zkSync Era and StarkNet lead this space. The trade-off? Generating these proofs is computationally expensive and complex to develop.
How Fraud Proofs Actually Work
If you are using an Optimistic Rollup, you need to understand what happens when things go wrong. A fraud proof is not just a complaint; it is a precise technical execution. When a sequencer posts a batch of transactions to Ethereum, they include a new "state root." If this state root is wrong-meaning the balances or contract states don't match reality-anyone can step in.
- Dispute: A verifier submits a claim that the state transition is invalid.
- Replay: The protocol forces the sequencer to prove the exact steps of the disputed transaction on the Ethereum mainnet.
- Verification: If the replay matches the claimed state, the proof fails, and the verifier wins. If the replay shows an error, the sequencer is penalized, and the state is corrected.
This process consumes significant gas. Recent benchmarks show a single fraud proof can cost between 500,000 and 1,000,000 gas units on Ethereum. That’s why only serious errors trigger this mechanism. For most users, the existence of this threat is enough to keep sequencers honest. However, if you hold large amounts of assets on an Optimistic Rollup, you must wait out the challenge period (typically 7 days, though some newer chains have reduced this to hours) before withdrawing back to Layer 1 to avoid any theoretical risk.
ZK Proofs: Speed vs. Complexity
ZK Rollups flip the script. Here, the burden of proof is on the prover, not the challenger. Every time a batch is submitted, a specialized computer generates a small piece of data-the proof-that proves the entire batch was computed correctly without revealing the underlying data.
The verification of this proof on Ethereum is incredibly fast, often taking less than a second. Because the math guarantees correctness, there is no need for a multi-day challenge window. This makes ZK Rollups ideal for applications where speed and finality matter, like high-frequency trading or gaming. However, the infrastructure required to generate these proofs is heavy. A single proof generation server can cost upwards of $15,000, and developers face a steep learning curve involving advanced cryptography. As of late 2023, advancements in PLONK and Halo2 circuits have made general-purpose ZK computing more viable, but it remains harder to build than its optimistic counterpart.
| Feature | Optimistic Rollups | ZK Rollups |
|---|---|---|
| Security Mechanism | Fraud Proofs (Challenge Period) | Validity Proofs (Cryptographic Verification) |
| Finality Time | 7 Days (Standard) / Hours (Newer Chains) | Near-Instant (Under 10 Minutes) |
| Data Posted to L1 | Full Transaction Data + State Root | Validity Proof + Minimal Data |
| Development Complexity | Medium (Solidity/EVM focused) | High (Cryptography/Circuit Design) |
| Gas Cost per Tx (L1 Data) | $0.03 - $0.15 | Lower (30-50% reduction due to smaller proofs) |
| Key Examples | Arbitrum, Optimism, Base | zkSync Era, StarkNet |
Real-World Risks and Vulnerabilities
No system is perfect. While rollups inherit Ethereum's base layer security, the implementation details introduce unique risks. In October 2023, the Degen Chain incident highlighted how delayed batch data publishing could cause 12-hour reorganizations, confusing users about their actual balance. Similarly, subtle bugs in fraud proof mechanisms have been documented by security researchers. One notable theoretical attack showed that a flaw in state root verification could allow invalid transitions to finalize if not caught during the challenge window.
Another emerging threat is cross-rollup interoperability. As different rollups try to talk to each other, timing differences in settlement layers can create vulnerabilities. An attacker might exploit the gap between when one rollup considers a transaction final and when another does. To address this, the Ethereum Research community is developing standardized security stages, moving from basic validity guarantees to global ordering guarantees. Until these standards are fully implemented, users should be cautious with bridges connecting different rollup ecosystems.
What This Means for You
So, which one should you use? If you are a developer building a new dApp, consider your priorities. Need quick development and broad compatibility? Go with an Optimistic Rollup using the OP Stack or Arbitrum Nitro. Need instant finality and lower long-term data costs? Invest in the complexity of a ZK Rollup. For end-users, the choice matters less for daily spending but significantly for large withdrawals. If you are moving millions of dollars, check the withdrawal delay of your chosen chain. On Arbitrum, that 7-day wait is real. On zkSync, you can withdraw almost immediately after the proof is verified.
As Ethereum continues to scale, with projects like JPMorgan using Optimistic Rollups for interbank settlements, the security models are maturing. The introduction of EIP-4844 (Proto-Danksharding) in 2024 will further reduce data costs, making both types of rollups even more efficient. Whether through the adversarial nature of fraud proofs or the mathematical elegance of zero-knowledge proofs, the goal remains the same: let you transact fast without sacrificing the safety of the Ethereum mainnet.
What is the main difference between a fraud proof and a validity proof?
A fraud proof assumes a transaction is valid until someone proves it is wrong within a set time frame. A validity proof provides immediate mathematical evidence that the transaction is correct, requiring no waiting period for challenges.
Do I need to wait 7 days to withdraw from all Layer 2 networks?
No. Traditional Optimistic Rollups like Arbitrum and Optimism typically require a 7-day challenge period for withdrawals to Layer 1. However, ZK Rollups offer near-instant finality, and some newer Optimistic implementations have shortened this window to just a few hours.
Which is more secure: Optimistic or ZK Rollups?
Both inherit Ethereum's security, but they differ in risk profiles. ZK Rollups are theoretically stronger because correctness is mathematically guaranteed. Optimistic Rollups rely on the assumption that at least one honest verifier will catch errors during the challenge period. In practice, both are considered highly secure when properly implemented.
How much does it cost to run a fraud proof?
Submitting a fraud proof on Ethereum can consume between 500,000 and 1,000,000 gas units. Depending on current gas prices, this can cost hundreds or thousands of dollars, which acts as a deterrent against frivolous disputes.
Are ZK Rollups harder to build than Optimistic Rollups?
Yes. ZK Rollups require expertise in advanced cryptography and circuit design (like PLONK or Halo2), whereas Optimistic Rollups primarily require standard Solidity and EVM knowledge. This higher barrier to entry means fewer teams are currently building ZK solutions compared to Optimistic ones.

Darren Moon
August 19, 2026 AT 02:02One must observe the profound inadequacy of this exposition regarding the actual computational overhead of state verification in optimistic rollups. The assumption that a seven-day window is merely a 'waiting period' ignores the intricate gas auction dynamics that occur during dispute resolution, which are often underreported in such high-level summaries. Furthermore, the juxtaposition of ZK and Optimistic models fails to account for the specific latency introduced by circuit compilation times in production environments, a detail crucial for institutional adoption. It is rather tedious to read through paragraphs that rehash basic concepts without delving into the nuances of data availability layers. The mention of JPMorgan feels like a hollow attempt at legitimacy without citing specific throughput metrics or settlement finality guarantees relevant to interbank clearing. One expects a deeper analysis of how EIP-4844 specifically alters the cost-benefit ratio for posting full transaction data versus compressed proofs. The table provided is superficially useful but lacks the critical dimension of auditability depth for each protocol. Without understanding the exact cryptographic assumptions behind STARKs versus SNARKs, the reader remains in a state of comfortable ignorance. This piece serves more as marketing copy than a technical breakdown for developers who need to make architectural decisions today. The phrase 'mathematical certainty' is bandied about with a casualness that borders on negligence given the history of zero-knowledge proof bugs. Ultimately, one is left wondering if the author has ever actually deployed a verifier contract or interacted with a sequencer's API directly.
Quang Thai Tran
August 19, 2026 AT 15:22The narrative here is suspiciously aligned with the interests of those who profit from the current centralized sequencer model. Notice how they emphasize 'security inherited from Ethereum' while conveniently glossing over the fact that the sequencer holds unilateral power over ordering and censorship until the challenge period expires. This is not just a technical flaw; it is a structural conspiracy to maintain control over user funds. The 'fraud proof' mechanism is merely a theatrical performance designed to give users a false sense of security while the real power remains with the few. Why do we trust these 'verifiers' when they are often employed by the same entities running the rollup? The shift to ZK is not about efficiency; it is about removing the human element of trust entirely because they know we will eventually catch on. The Degen Chain incident was no accident; it was a controlled burn to test our patience before they tighten the screws further. We must look beyond the code and see the hand of the centralizers manipulating the timeline. Every millisecond of delay in finality is a second where your assets are technically theirs. The promise of 'instant finality' in ZK is a trap for the uninitiated, hiding the complexity of proof generation servers that could be points of failure. Do not let the polished language fool you into believing this is a decentralized solution. It is a new layer of opacity built on top of an already opaque system.
Kate Staab
August 20, 2026 AT 05:21It is truly disgraceful that so many people fall for this hype without reading the fine print! The idea that you can just send money and expect it to be safe is morally bankrupt thinking. Where is the accountability when the sequencer decides to hold your funds hostage for a week? It shows a complete lack of respect for the average person's time and resources. We need to stop treating these tech solutions as magic and start demanding real transparency. If they cannot guarantee immediate access to your own money, they have no right to call it 'secure'. This whole industry needs to grow up and take responsibility for its reckless speed. It is dramatic enough that we are betting our life savings on complex math that even the creators barely understand. Stop pretending that a 'challenge period' is a feature and not a bug! Until every single transaction is instantly final and verifiable by anyone, we are all just playing with fire.
Calliope Clio
August 21, 2026 AT 08:40Oh, darling, did you really think explaining gas costs would impress the elite? 🧐 The true connoisseur knows that the *vibe* of the blockchain matters far more than the dry mechanics of fraud proofs. It’s simply adorable how everyone gets worked up over withdrawal delays when the real art is in the speculation. 📉✨ One must appreciate the elegance of a well-timed rug pull, after all. These 'security models' are just fancy words for how long you can keep your eyes closed before the music stops. Don’t worry about the math, honey; just worry about whether your portfolio looks chic enough for the next bull run. 💅🚀
Tasha Davis
August 21, 2026 AT 19:00This is SO helpful! I always get confused by all the crypto stuff but this made it click! 🌟 Thank you for breaking it down so simply. I never knew there was such a big difference between the two types of rollups. Now I feel much smarter about my investments! Keep up the great work! 😊
Abigail Sparks
August 22, 2026 AT 19:10Let's cut through the noise here: if you're moving serious capital, the 7-day wait on Optimistic Rollups is a non-starter for most DeFi strategies. You don't get to play games with liquidity constraints when APYs are fluctuating daily. ZK Rollups aren't just 'faster'; they are fundamentally changing the risk profile by eliminating the window of uncertainty. Stop accepting 'good enough' security when mathematical certainty is available. The infrastructure costs are dropping, and the learning curve is flattening. Get ahead of the curve or stay stuck in the past. The future belongs to those who demand instant finality. Don't let legacy protocols slow you down. Act now.
OLIVER CHRISTIAN
August 23, 2026 AT 21:17Great overview, but I’d love to see more on the interoperability aspect mentioned briefly. As cross-chain bridges become more common, the timing mismatch between different L2s is a huge pain point. Have you seen any recent updates on standardizing these settlement windows? It seems like a critical area for improvement. Otherwise, solid explanation of the basics.
Kelsey Anne
August 25, 2026 AT 04:08Fraud proofs are weak. Validity proofs are strong. End of story. Anything less is gambling.
Mike Baca
August 26, 2026 AT 15:57Man, this got me thinking abt the philosophical implications of trust vs verification. Like, are we really trusting the math or just the people who wrote the code? Its kinda wild how much faith we put in these circuits. But hey, if it works, right? Maybe we shouldnt worry so much about the black box nature of it all. Just vibes and math. Pretty cool concept tho. Makes me feel hopeful for the future of finance. Who knew proving truth could be so complicated yet so simple at the same time? Love the energy here. 🤔
Teri W
August 27, 2026 AT 17:48OMG, finally someone explained this without making me feel stupid! But seriously, who decided that waiting 7 days is normal? That's insane! My bank doesn't even take that long to clear checks anymore. It's like we're living in the stone age with this tech. Can we please just fix this already? The drama of trying to move funds is exhausting. We need better! 🙄